Understanding the Query: settimeout("alert('xss')", 2000)
The string settimeout("alert('xss')", 2000) is a classic proof-of-concept payload used to demonstrate a cross-site scripting (XSS) vulnerability. In JavaScript, setTimeout() schedules a function to run after a specified delay in milliseconds. When a web application accepts user input and later renders it into a page without proper sanitisation or encoding, an attacker can inject a script like this. Here, the browser would display an alert box reading "xss" two seconds after the page loads — a harmless demonstration, but the same technique can be used to steal session cookies, redirect users, or exfiltrate data.
The key lesson is that XSS is an application-layer problem, not a hardware one. No processor, operating system, or industrial computer can "block" a script that a web application itself chooses to execute. What hardened hardware and a controlled operating system can do is reduce the attack surface, enforce application allow-listing, and prevent an exploited browser session from reaching the rest of the system.
Why This Matters for Industrial and Kiosk Deployments
Industrial PCs, thin clients, and all-in-one terminals frequently run browser-based dashboards, HMI panels, digital signage, and self-service kiosks. These are exactly the environments where XSS payloads cause real damage: a compromised kiosk can leak customer input, tamper with displayed content, or act as a pivot point into a plant network. Defending against this requires a layered approach.
| Layer | Mitigation | Example |
|---|---|---|
| Application | Output encoding, Content Security Policy (CSP), input validation | Escape HTML entities; set script-src 'self' |
| Browser | Locked-down kiosk mode, no extensions, auto-restart | Chromium kiosk flags, restricted URLs |
| Operating System | Minimal image, no local admin, read-only filesystem | Windows 11 IoT, embedded Linux |
| Hardware | No user-accessible ports, fanless sealed enclosure | Industrial PC with restricted I/O |
A Content Security Policy that disallows inline scripts would block settimeout("alert('xss')", 2000) from executing at all, because the injected handler would violate the policy. Combined with a read-only OS image, any successful injection cannot persist across a reboot.
Practical Hardening for Browser-Based Terminals
For kiosks and industrial terminals, the recommended baseline is: run the browser in kiosk mode against a fixed allow-list of URLs, disable developer tools and extensions, apply a strict CSP at the web server, and configure the machine to reboot on a schedule so any tampering is wiped. Deploy the terminal on an operating system image that does not expose a general-purpose desktop, and remove or disable unused USB and network services.
Where the application cannot be fully trusted, network segmentation isolates the terminal from back-end systems. The terminal should reach only the specific web services it needs, so even a successful XSS cannot be used to scan or reach internal infrastructure.
Thinvent Products Suited to Hardened Deployments
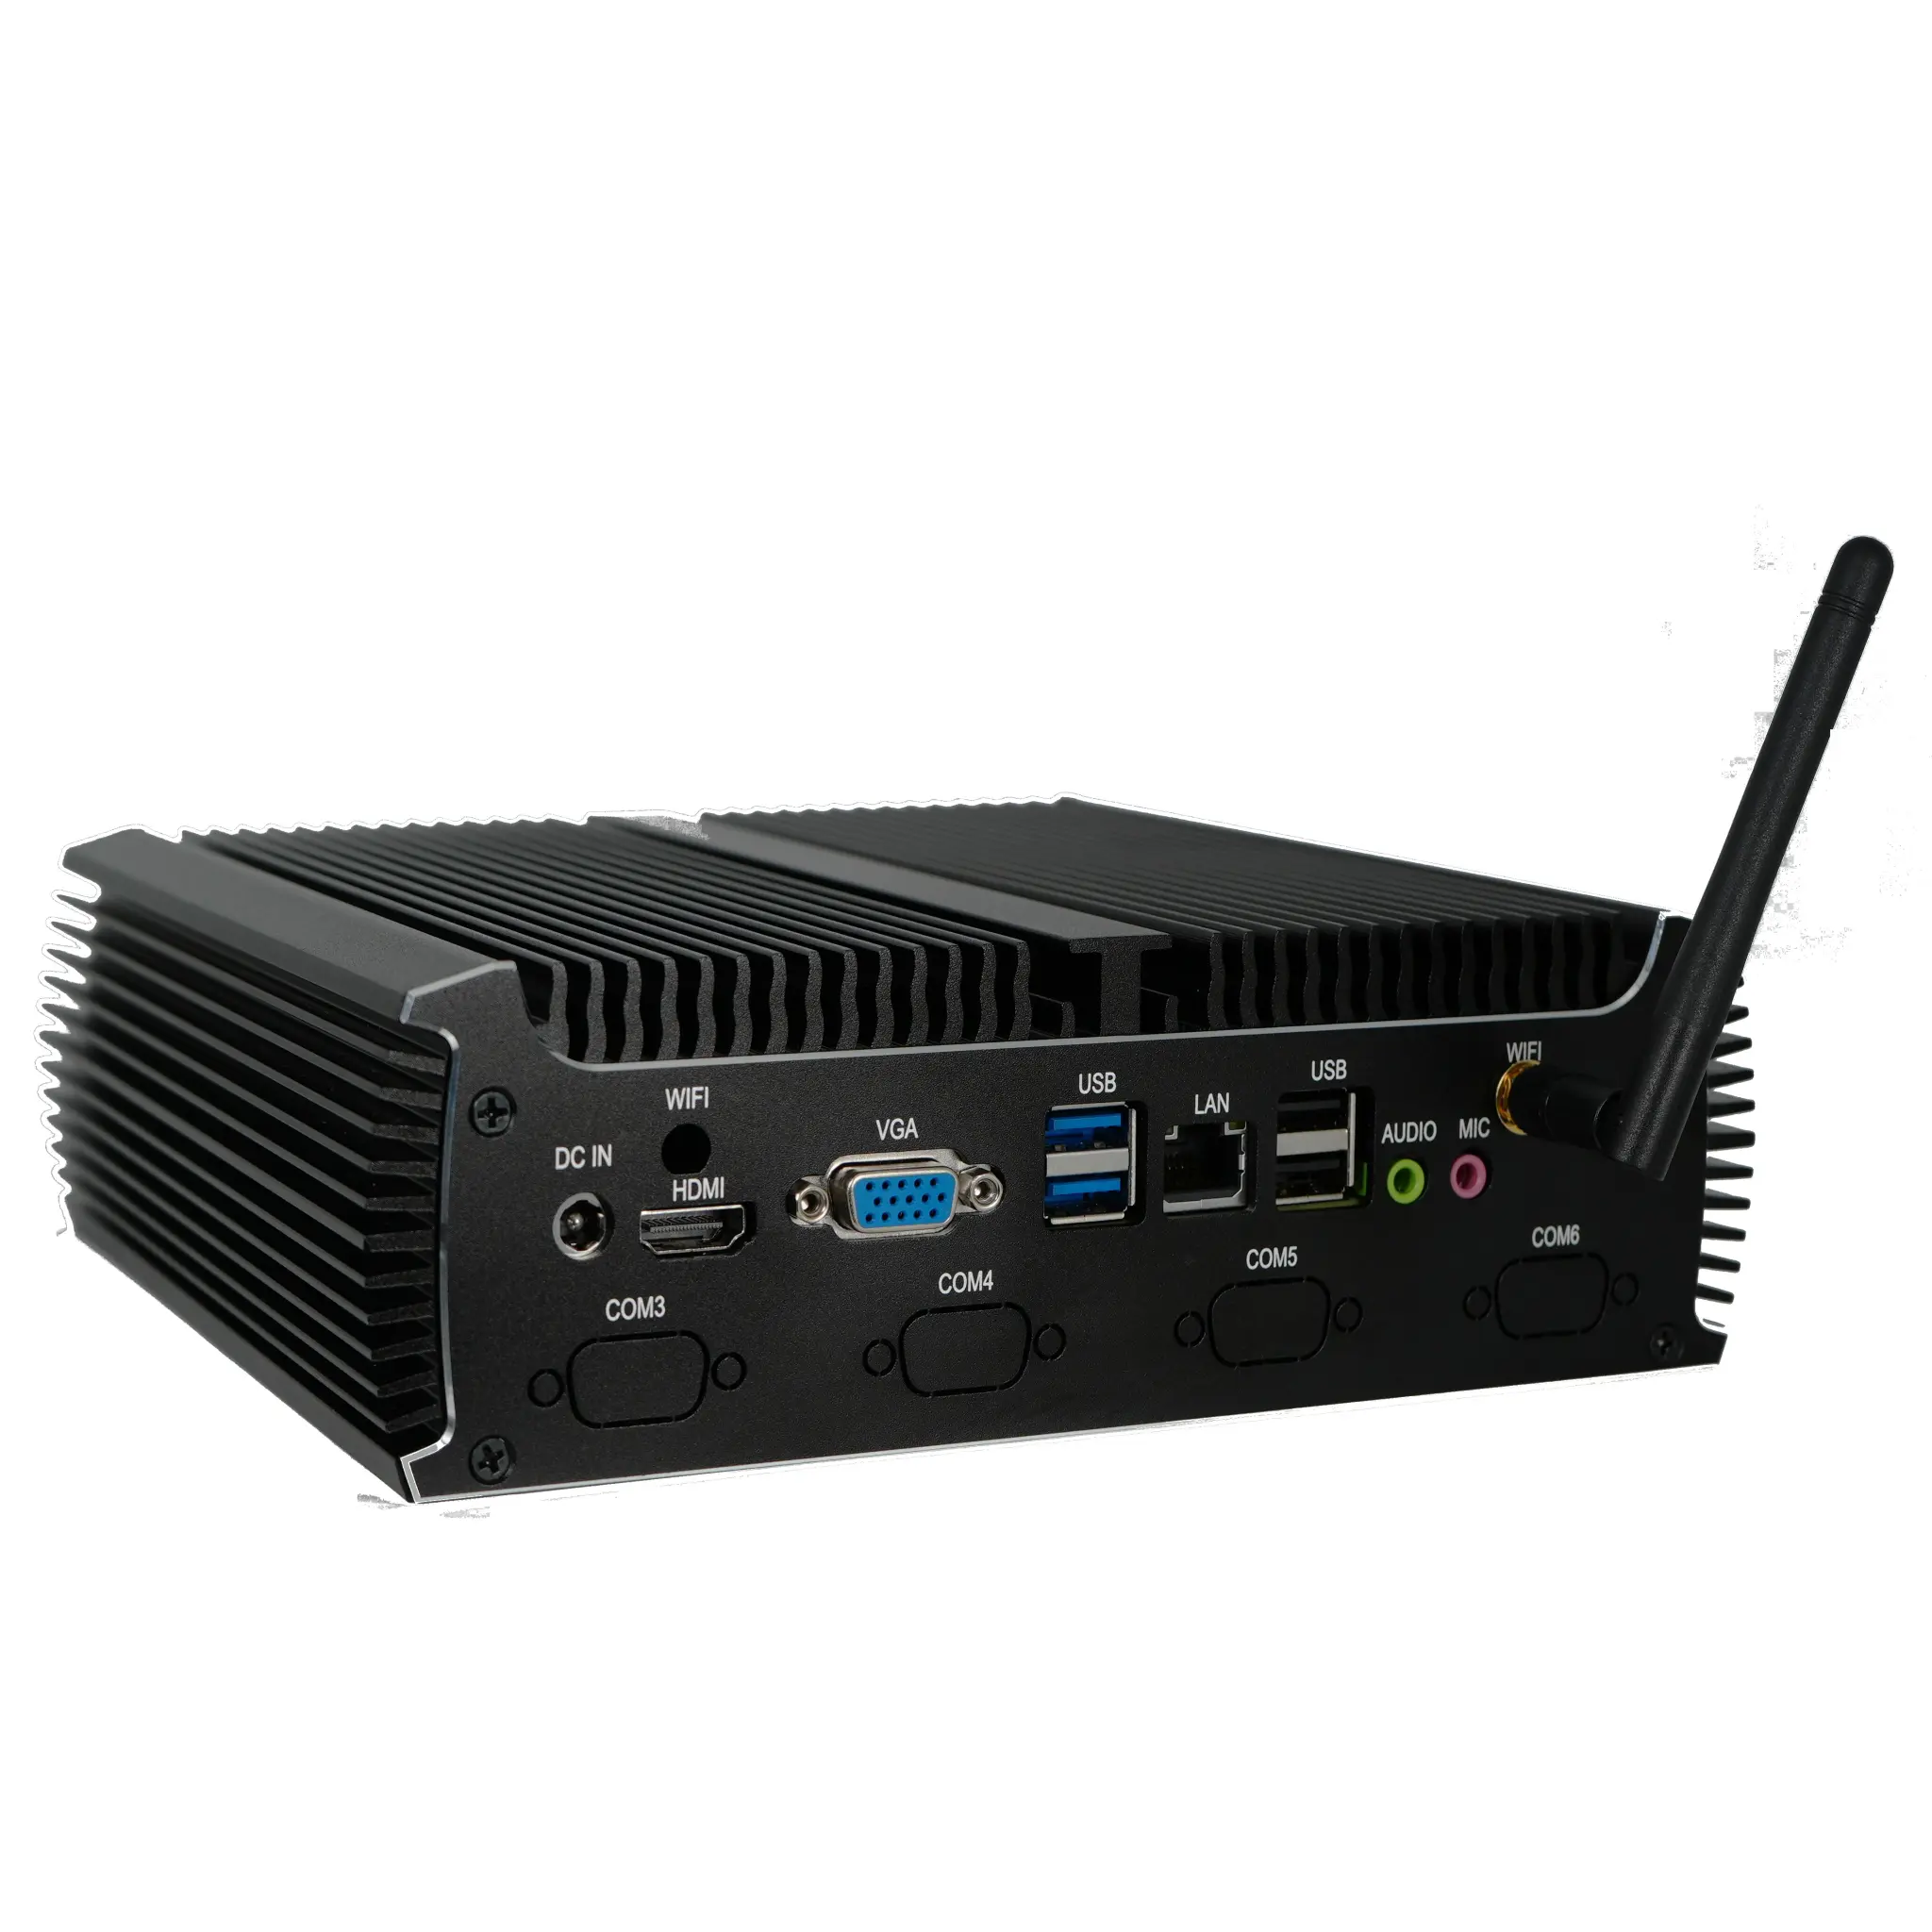
Thinvent's industrial computers, mini PCs, thin clients, and all-in-one PCs are built for exactly these controlled environments. Fanless, sealed chassis reduce physical tampering and dust ingress, while support for Windows 11 IoT, Thinux™ Embedded Linux, and diskless or read-only configurations allows administrators to lock down the OS image. Quad DB9 serial variants connect legacy industrial equipment without adding general-purpose expansion, and dual Ethernet options support network segmentation between the terminal and the plant network. For kiosk and signage deployments, Thinvent all-in-one PCs provide an integrated display and compute unit that can be configured with a minimal OS and kiosk-mode browser, giving IT teams a consistent, manageable platform for secure browser-based applications.